Security and code ownership
Your accounts, your code, and secrets that never reach the client.
Acasa Labs builds with your accounts from the first day: repositories, cloud, app stores, and credentials sit in your organization, not ours. In the software itself, secrets stay on the server, access rules are enforced in the database, and AI runs on your own infrastructure when data must not leave it. These are practices from systems we run, such as NoteTube and GymFast.
The problem
The riskiest part of outsourcing is what you cannot see.
Code in the vendor's GitHub. A cloud account in the agency's name. API keys pasted into a mobile app. Access rules that live only in the frontend, so one changed request reads another customer's data. Most of these problems are invisible until the day you change vendors or something leaks. They are cheap to prevent at the start and expensive to fix later.
What we build
- 01
Your accounts from day one
GitHub, cloud, domain, app store, payment, and analytics accounts are created in your organization. We are members you can remove, not owners you have to negotiate with.
- 02
Secrets stay on the server
API keys, model keys, and admin credentials live in server environments and secret managers, never in a web bundle or a mobile app.
- 03
Access enforced where it cannot be skipped
Roles and tenant isolation enforced in the database or one backend layer, with tests that try to read data that is not theirs.
- 04
Data that stays where it must
When documents, footage, or records must not leave your network, the AI runs on your infrastructure instead of a third-party API.
From production
Security decisions from systems we run.
Model keys never reach the client
NoteTubeNoteTube's AI keys live only in a separate FastAPI service. The web and mobile clients never see them, and its remote MCP server checks OAuth tokens for the right audience.
Roles in the database
GymFastGymFast's six-level role hierarchy, from owner to member, is enforced with Postgres row-level security rather than in app code.
Inference that stays local
Acasa SentinelAll of Acasa Sentinel's inference runs locally. No footage or number plate is sent to a third-party API.
Write paths the public cannot reach
Siona JewelsSiona Jewels' enquiries are created only by a server action behind Turnstile, a honeypot, and a fill-time check. The public API cannot write them.
Honest trade-offs
What we do not claim
We are a small team, not a certified enterprise vendor. We do not hold SOC 2 or ISO 27001 certification. If your procurement requires a certified supplier, we will say so early. If it needs a security questionnaire, a data processing agreement, or an NDA, we are glad to work through it.
What we reach for
- Accounts in your organization
- Secret managers and server-only keys
- Postgres row-level security
- OAuth with audience checks
- Cloudflare Turnstile
- Local and on-premise AI
Proof
Shipped, not pitched.
01Our product
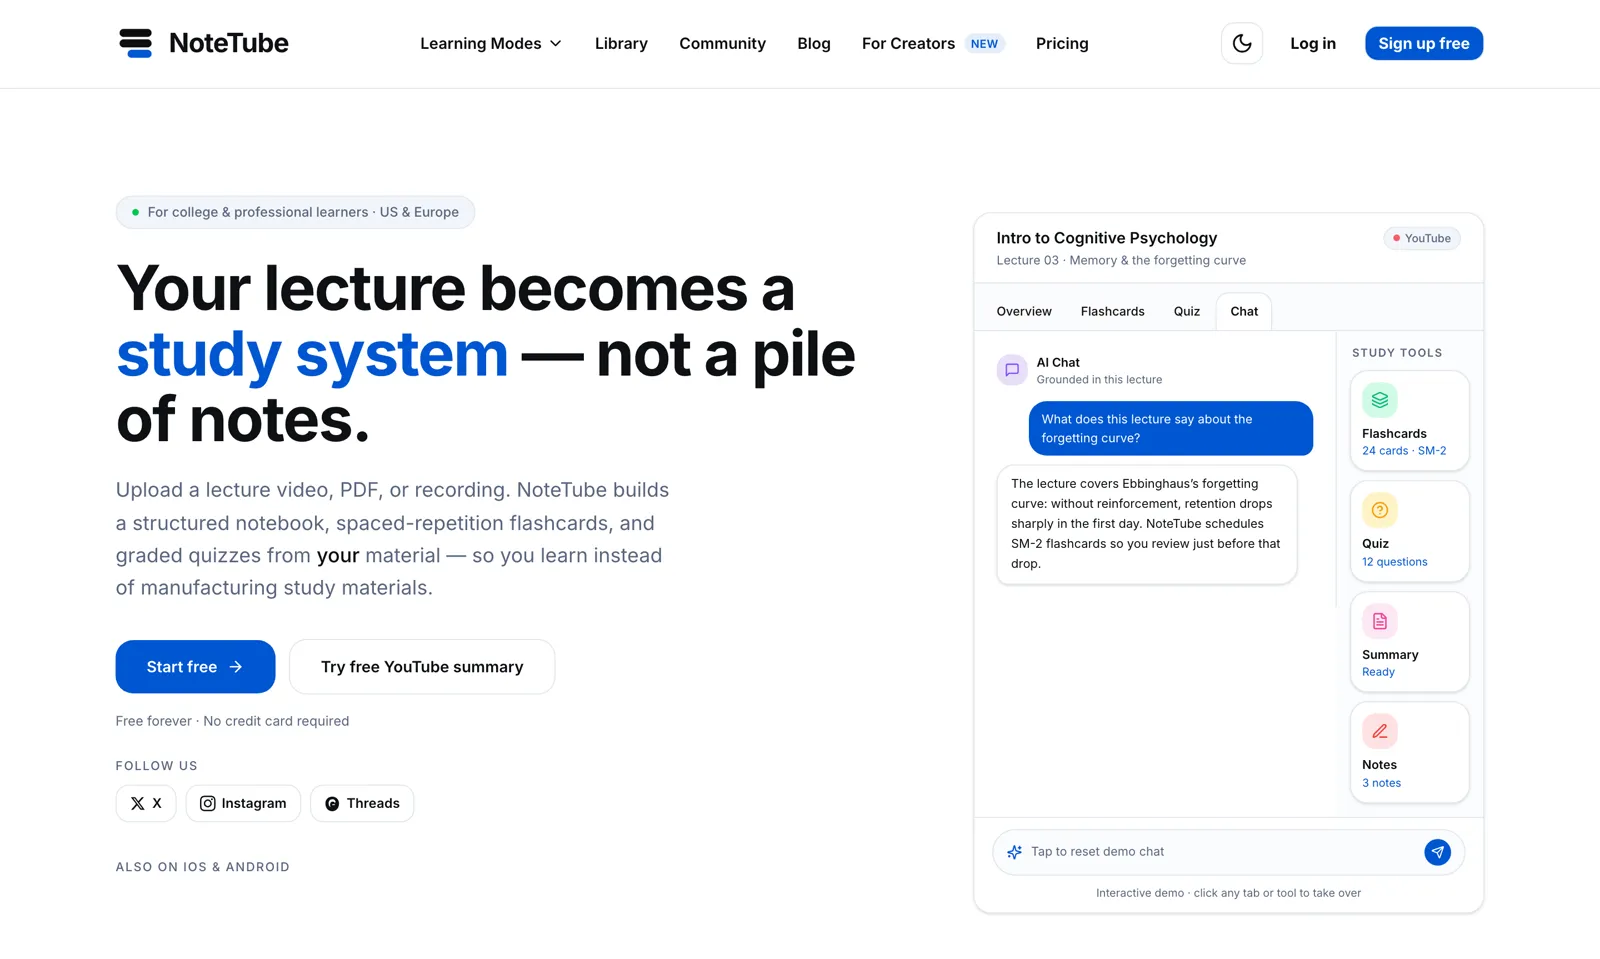
NoteTube
A lecture becomes a study system: chat, flashcards, quizzes, all grounded in the source.
An AI learning platform that turns PDFs, YouTube lectures, recordings, and notes into a structured notebook with grounded chat, spaced-repetition flashcards, and graded quizzes.
Web · iOS · Android · Chrome extension · MCP server
02Our product
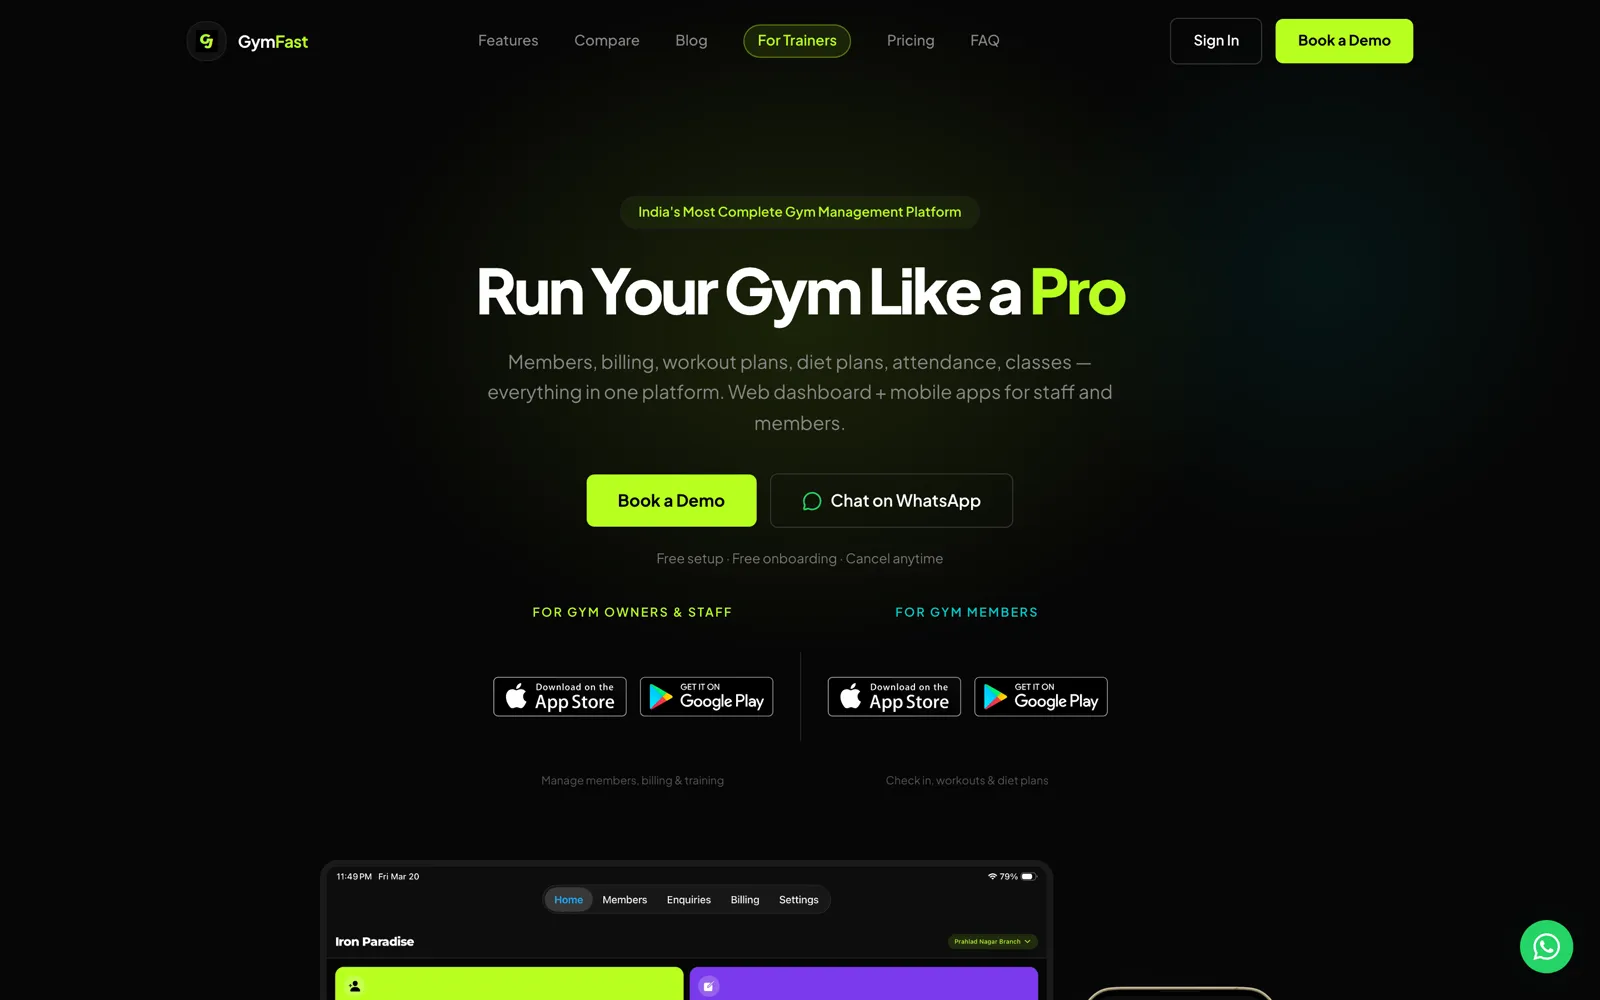
GymFast
Members, billing, classes, and workout plans for a gym, in one platform and three apps.
Gym management software for gym owners and personal trainers. A web dashboard and a staff app run members, plans, invoices, enquiries, and classes; members get their own branded app; GymFast Pro gives independent trainers the same tools for their clients.
Web dashboard · iOS · Android · Staff, member, and trainer apps
03Case study
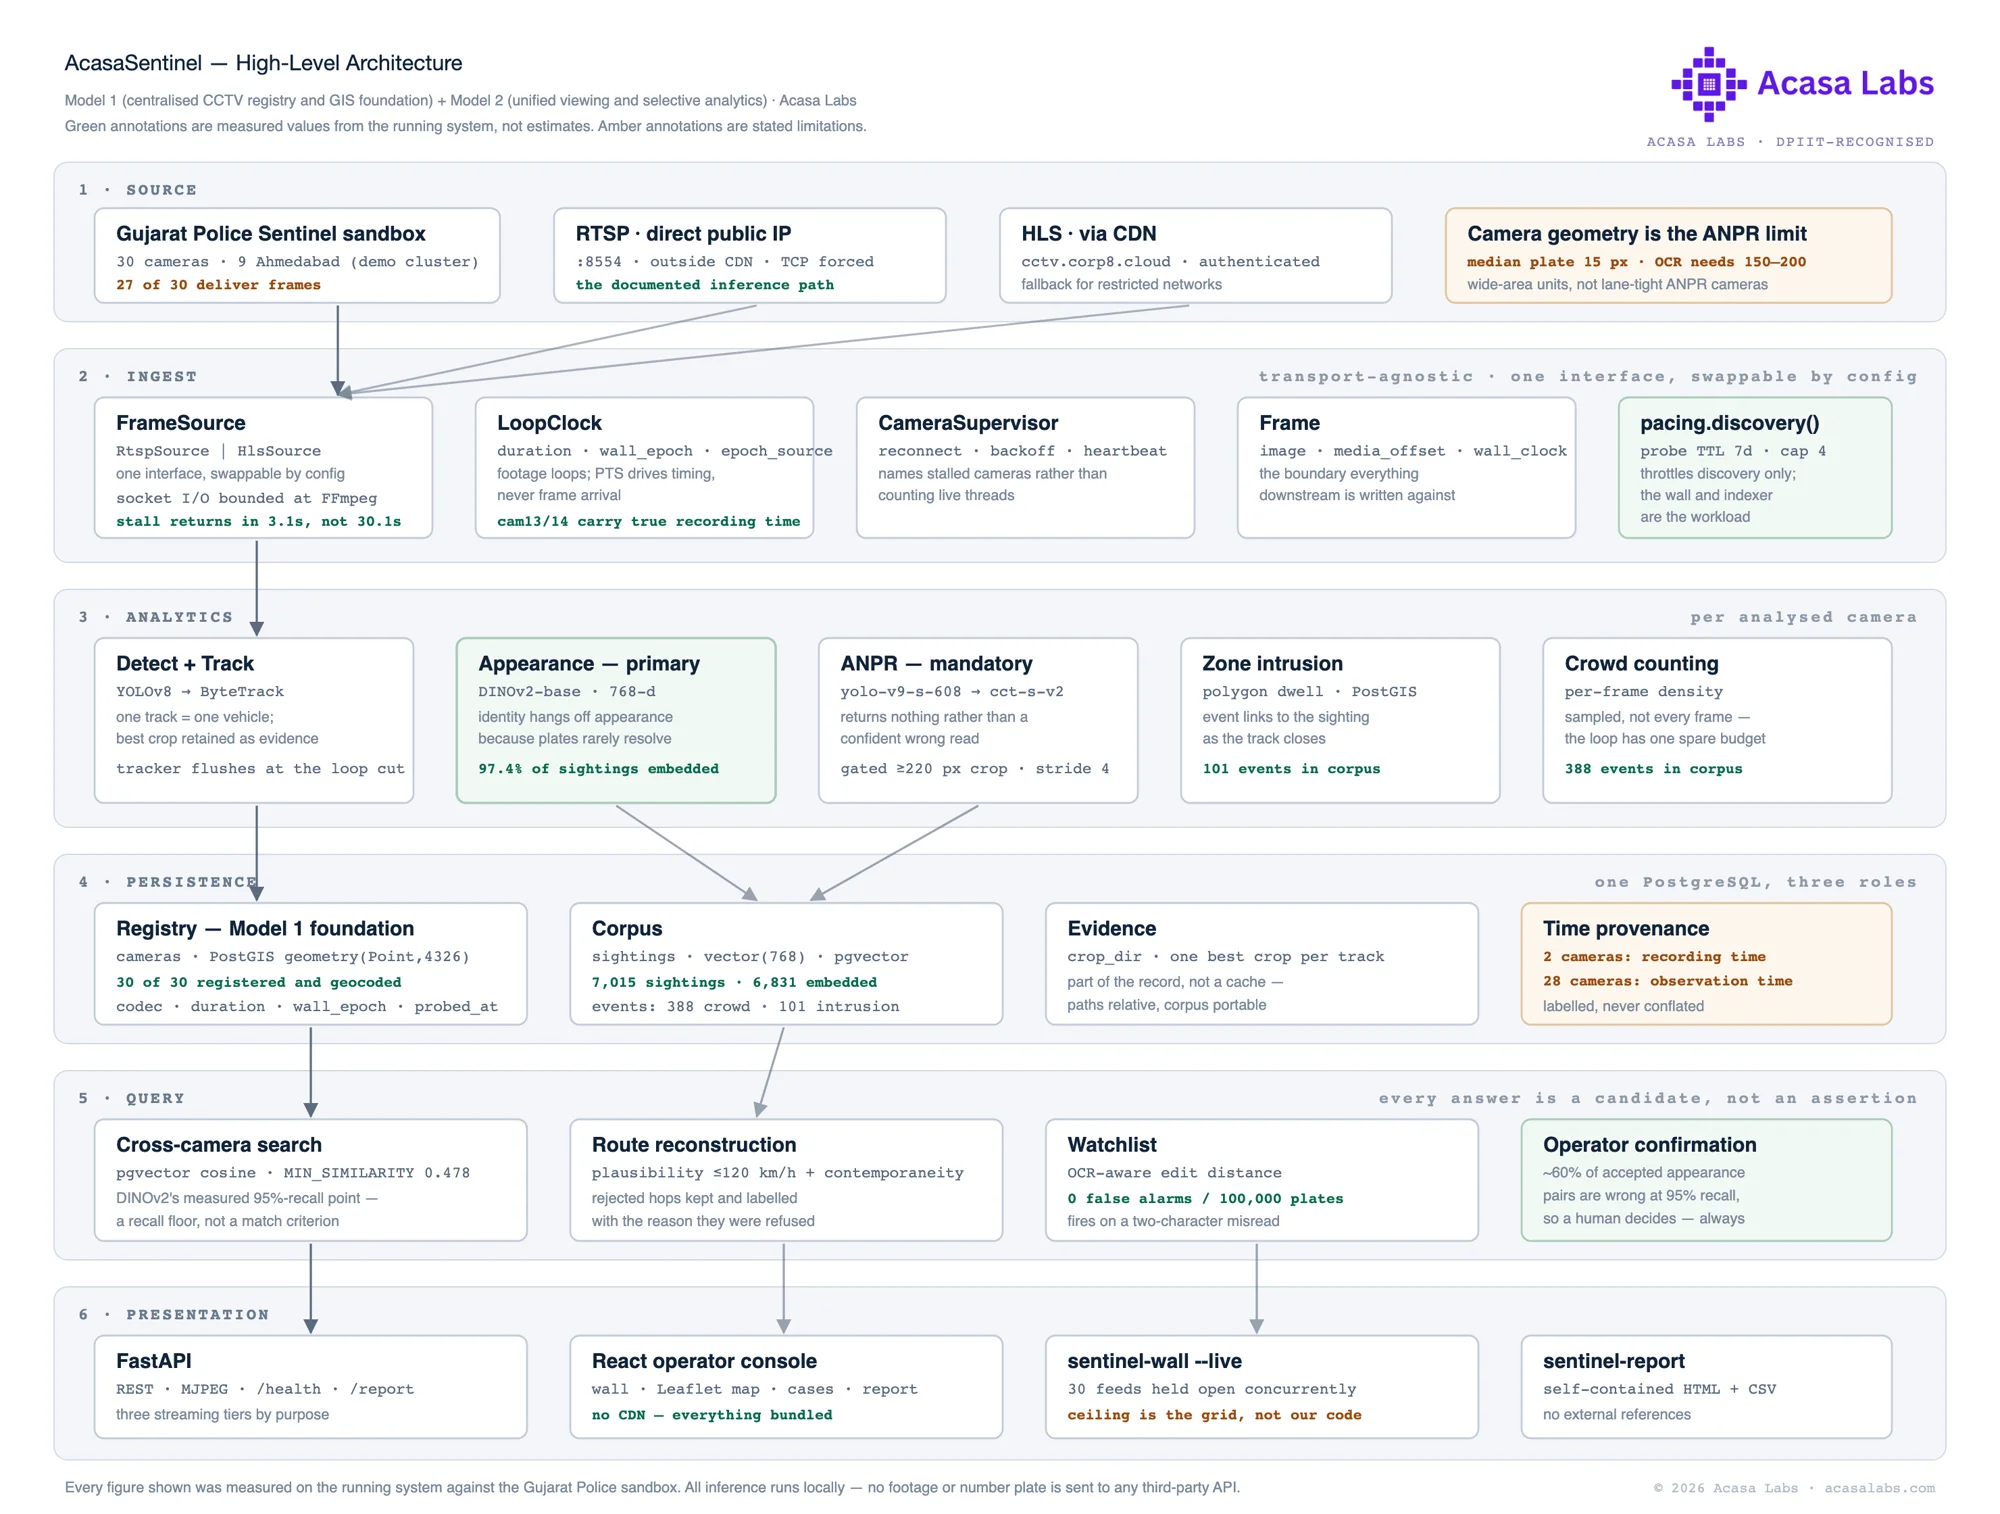
Acasa Sentinel
Give it a number plate. It returns the vehicle's route across a CCTV network.
A vendor-neutral video analytics system built for the Gujarat Police Hackathon Innovation Challenge 2026. It reads number plates, re-identifies vehicles by appearance across cameras, reconstructs routes, and raises watchlist alerts for an operator to confirm.
Operator console (web) · API
Questions
Security questions we get asked.
Who owns the code and the accounts?
You do, from the first day. Repositories, cloud, app store, and payment accounts are in your organization. If we stop working together, you remove our access and nothing needs handing over.
Will you sign an NDA?
Yes. We can sign your NDA before you share anything sensitive, or provide ours.
How do you handle our credentials?
We ask for access through your own accounts and roles rather than shared passwords, keep secrets in server environments, and never put keys in a web or mobile client.
Can the AI run without sending our data to OpenAI or another provider?
Yes. The pipeline and an open-weight model can run in your cloud or on your hardware. Acasa Sentinel runs all of its inference locally for this reason.
Are you SOC 2 or ISO 27001 certified?
No. We follow the practices on this page and are happy to answer a security questionnaire, but we are not a certified vendor.
Security and code ownership
Have a security questionnaire?
Send it with the project. We will answer it honestly, including the parts where a certified vendor would be a better fit.